What Is an Identity Provider (IdP)?
An Identity Provider (IdP) is a trusted system that authenticates users or applications and provides identity information/tokens that other applications and APIs can trust.
Examples include:
- Microsoft Entra ID
- Keycloak
- Auth0
- Okta
- Google Identity
- Duende IdentityServer
The easiest way to remember:
Identity Provider = the system responsible for establishing "Who are you?"
1. Why Do We Need an Identity Provider?
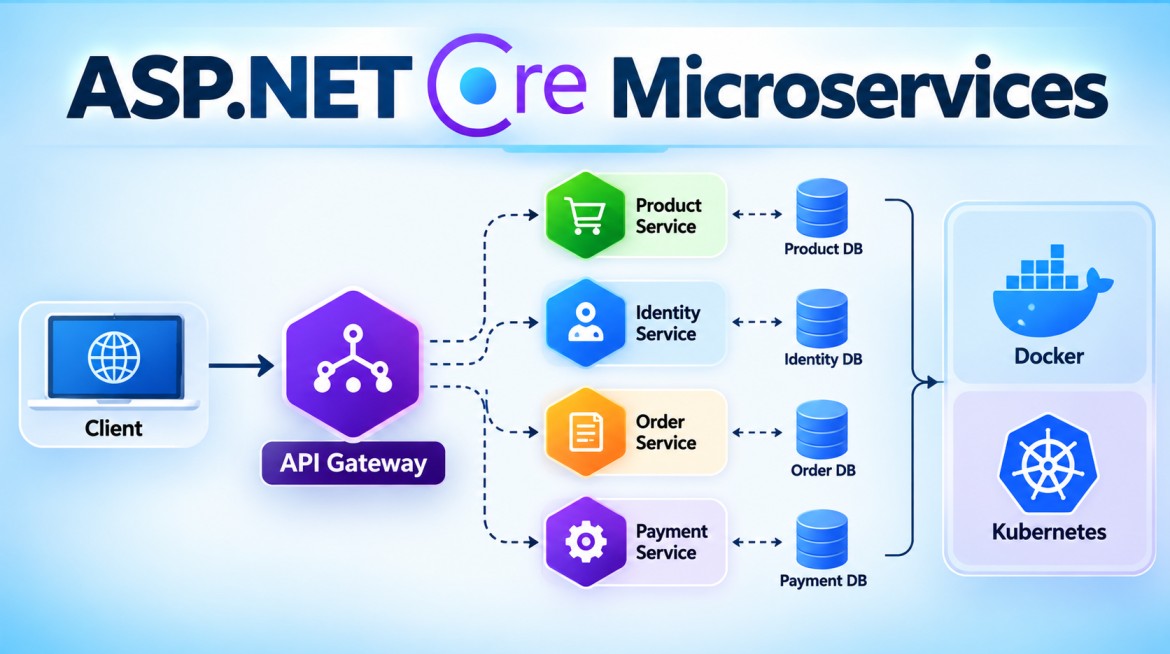
Imagine a microservices system:
Angular
   |
   +----> Order Service
   +----> Product Service
   +----> Payment Service
   +----> Inventory Service
Without centralized identity, every service might implement:
Order Service
    -> Login
    -> Password validation

Payment Service
    -> Login
    -> Password validation

Product Service
    -> Login
    -> Password validation
This duplicates security logic.
Instead:
                    Identity Provider
                          |
                     Authentication
                          |
                     Issues Tokens
                          |
                          v
User ---> Angular ---> API Gateway
                          |
                 +--------+--------+
                 |        |        |
                 v        v        v
               Order   Product   Payment
The microservices trust tokens issued by the configured Identity Provider.
2. Main Purpose
An Identity Provider centralizes identity-related responsibilities such as:
User Authentication
        +
Application Authentication
        +
Token Issuance
        +
Identity Claims
        +
Single Sign-On
        +
MFA
        +
Federation
Instead of every application building its own authentication system.
3. Basic Authentication Flow
Suppose a user opens an Angular application.
User
 |
 | Login
 v
Angular
 |
 | Redirect
 v
Identity Provider
 |
 | Verify credentials
 | MFA if required
 v
Authentication successful
 |
 | Tokens
 v
Angular
The client can then call an API using an access token:
Angular
   |
   | Authorization:
   | Bearer <access_token>
   v
Order API
Order API does not normally validate the user's password.
It validates the trusted token.
4. Identity Provider vs Your Web API
This distinction is important.
Identity Provider
Responsible for:
Who are you?For example:
User = SyedOrder API
Responsible for:
What can this identity do
inside Order Service?
For example:
orders.read      ✓
orders.create    ✓
orders.delete    ✗
So:
Identity Provider
      |
      | Authentication
      v
   Identity
      |
      v
Order Service
      |
      | Authorization
      v
Protected Resource
5. What Does the IdP Actually Do?
When a user logs in:
Username
Password
MFA
Certificate
Passkey
etc.
the IdP verifies the authentication method.
If successful, it establishes an identity:
User ID = 1001
Name    = Syed
Roles   = Admin
It can then issue tokens according to OAuth/OIDC configuration.
6. Tokens Issued by an Identity Provider
Depending on the protocol and flow, you may encounter:
ID Token
Used by the client as part of OpenID Connect authentication.
Identity Provider
       |
       | ID Token
       v
Client Application
It answers:
Who authenticated?
Access Token
Used for accessing a protected API.
Identity Provider
       |
       | Access Token
       v
Client
       |
       | Access Token
       v
Web API
It represents authorization granted for the protected resource.
Refresh Token
Where the selected flow/client type permits it, a refresh token can be used to obtain new access tokens without requiring the user to perform a fresh interactive login each time.
Refresh Token
     |
     v
Identity Provider
     |
     v
New Access Token
7. Identity Provider with OAuth and OIDC
This connects your previous topics.
                Identity Provider
                      |
          +-----------+-----------+
          |                       |
          v                       v
      OAuth 2.0                 OIDC
          |                       |
          v                       v
    Authorization           Authentication
          |                       |
          v                       v
    Access Token              ID Token
So:
OAuth 2.0
    = Authorization framework

OIDC
    = Authentication layer

Identity Provider
    = System implementing/providing
      identity services

JWT
    = Token format
These terms are related, but they are not the same thing.
8. Example with Microsoft Entra ID
Suppose your architecture is:
Angular
+
API Gateway
+
Order Service
+
Payment Service
You could use Microsoft Entra ID as the Identity Provider.
                     Microsoft Entra ID
                            |
                    OAuth 2.0 / OIDC
                            |
                            v
User ----> Angular Application
                 |
                 | Access Token
                 v
             API Gateway
                 |
                 v
            Order Service
Order Service trusts tokens issued by the configured Entra tenant/authority.
9. ASP.NET Core Configuration
For example:
{
  "Authentication": {
    "Authority": "https://login.microsoftonline.com/YOUR-TENANT-ID/v2.0",
    "Audience": "YOUR-API-CLIENT-ID"
  }
}
Then:
using Microsoft.AspNetCore.Authentication.JwtBearer;

var builder = WebApplication.CreateBuilder(args);

builder.Services.AddControllers();

builder.Services
    .AddAuthentication(
        JwtBearerDefaults.AuthenticationScheme)
    .AddJwtBearer(options =>
    {
        options.Authority =
            builder.Configuration["Authentication:Authority"];

        options.Audience =
            builder.Configuration["Authentication:Audience"];

        options.RequireHttpsMetadata = true;
    });

builder.Services.AddAuthorization();

var app = builder.Build();

app.UseHttpsRedirection();

app.UseAuthentication();
app.UseAuthorization();

app.MapControllers();

app.Run();
Package commonly used:
dotnet add package Microsoft.AspNetCore.Authentication.JwtBearer10. What Does Authority Mean?
This is important.
options.Authority =
    "https://login.microsoftonline.com/.../v2.0";
The authority identifies the trusted identity/token issuer configuration.
Conceptually:
Order Service

"I trust tokens associated with
this configured authority."
ASP.NET Core's JWT bearer handler can use the authority's published metadata/signing keys to validate incoming tokens.
11. How Does the API Trust the IdP?
The Identity Provider signs tokens.
Conceptually:
Identity Provider

Private Key
    |
    | Sign
    v
Access Token
    |
    v
Order API

Public Signing Key
    |
    | Verify
    v
Token accepted/rejected
The API validates things such as:
Signature
Issuer
Audience
Expiration
Then:
Valid
  |
  v
ClaimsPrincipal
  |
  v
Authorization
12. Identity Provider in Service-to-Service Authentication
Identity Providers are not limited to human users.
Suppose:
Order Service
      |
      v
Payment Service
Order Service can authenticate using an application/workload identity.
For example:
Order Service
      |
      | Client Credentials
      v
Identity / Authorization Server
      |
      | Access Token
      v
Order Service
      |
      | Bearer Token
      v
Payment Service
Here the token represents:
Order Servicerather than:
End User13. User Identity vs Service Identity
An identity system may therefore deal with both.
User
User
 |
 | Login
 v
IdP
 |
 | User Access Token
 v
API
Microservice
Order Service
 |
 | Application / Workload Identity
 v
Authorization Server
 |
 | Service Access Token
 v
Payment Service
14. Single Sign-On (SSO)
One major benefit of an IdP is Single Sign-On.
Without centralized identity:
Application A -> Login

Application B -> Login again

Application C -> Login again
With SSO:
                Identity Provider
                       ^
                       |
                   Login once
                       |
                     User
                  /    |    \
                 /     |     \
                v      v      v
             App A   App B   App C
Subject to the organization's session and authentication policies, the user can access multiple applications without repeatedly entering credentials.
15. Multi-Factor Authentication
The IdP can also centralize MFA.
For example:
Password
    +
Authenticator App
or:
Password
    +
Security Key
Applications don't need to independently implement every MFA mechanism.
16. Federation
An IdP can also participate in identity federation.
For example:
Your Application
       |
       v
Your Identity Platform
       |
       +---- Microsoft
       |
       +---- Google
       |
       +---- Corporate Identity System
This is useful for:
- enterprise SSO
- partner organizations
- external users
- social authentication
17. Identity Provider vs Authorization Server
These terms are related but not perfectly identical.
Identity Provider
Primarily concerned with:
Identity
Authentication
Authorization Server
OAuth terminology for the server that:
Authorizes clients
Issues access tokens
In modern platforms, the same product/service often performs both roles.
For example, a platform can provide:
OIDC
   -> Identity Provider behavior

OAuth 2.0
   -> Authorization Server behavior
Therefore developers often loosely refer to the whole platform as the Identity Provider.
18. Identity Provider vs API Gateway
Do not confuse these either.
| Identity Provider | API Gateway |
|---|---|
| Handles identity/authentication | Handles API entry/routing |
| Issues tokens | Can validate tokens |
| Supports OAuth/OIDC | Enforces gateway policies |
| User/application identities | Routes to microservices |
| SSO/MFA may live here | Rate limiting may live here |
Architecture:
              Identity Provider
                     |
                 Issue Token
                     |
                     v
Client ----------> Gateway
                     |
              Validate / Route
                     |
          +----------+----------+
          |                     |
          v                     v
      Order API             Product API
19. Identity Provider vs JWT
Another common interview question.
Identity Provider
        =
System / Service


JWT
        =
Token format
For example:
Microsoft Entra ID
       |
       | Issues
       v
JWT Access Token
The IdP is not the JWT.
20. Common Identity Providers
| Identity Provider / Platform | Typical environment |
|---|---|
| Microsoft Entra ID | Microsoft/Azure/enterprise |
| Keycloak | Open-source/self-hosted |
| Auth0 | Managed identity platform |
| Okta | Enterprise identity |
| Google Identity | Google identity ecosystem |
| Duende IdentityServer | .NET identity/OAuth/OIDC server scenarios |
The exact capabilities and licensing vary by product.
21. Advantages
Centralized authentication
Applications don't independently implement authentication.
Single Sign-On
Users can authenticate across multiple applications.
MFA
Centralized multi-factor authentication policies.
Standard protocols
Modern IdPs commonly support:
OAuth 2.0
OpenID Connect
and enterprise platforms may support additional federation protocols.
Token management
The identity platform handles token issuance and signing.
Microservices support
Multiple APIs can trust the same identity infrastructure while enforcing their own authorization.
Service identities
Services can authenticate independently from human users.
22. Disadvantages
Additional infrastructure
You need an identity platform.
Configuration complexity
You need to understand:
Client IDs
Scopes
Permissions
Redirect URIs
Issuer
Audience
Tokens
Certificates/Secrets
Central dependency
Authentication and new token acquisition depend on identity infrastructure availability.
Security-critical configuration
Incorrect redirect URIs, permissions, audiences, secrets, or token validation can create vulnerabilities.
23. Key Points
Remember these for interviews:
- IdP = Identity Provider.
- It authenticates identities.
- Identity may represent a user or workload/application.
- It can issue identity/security tokens.
- OIDC is commonly used for user authentication.
- OAuth 2.0 handles authorization/token-based API access.
- An ID Token is intended for the client.
- An Access Token is intended for the protected resource/API.
- APIs validate tokens rather than users' passwords.
- IdPs can provide SSO.
- IdPs can centralize MFA.
- Identity platforms can support federation.
- The IdP and API Gateway have different responsibilities.
- An IdP is not the same as JWT.
- A single identity platform may act as both an OIDC Identity Provider and an OAuth Authorization Server.
24. Interview Questions & Answers
Q1. What is an Identity Provider?
Answer:
An Identity Provider is a trusted system that authenticates users or applications and provides identity information or tokens that applications and APIs can trust.
Q2. What are examples of Identity Providers?
Examples include:
Microsoft Entra ID
Keycloak
Auth0
Okta
Google Identity
Q3. What is the difference between an IdP and an API Gateway?
Answer:
An Identity Provider handles identity, authentication, and token issuance. An API Gateway manages API traffic such as routing, rate limiting, and potentially token validation.
Q4. Does the Identity Provider issue JWTs?
It can. Many OAuth/OIDC identity platforms issue JWT-formatted ID tokens and may issue JWT-formatted access tokens.
However:
JWT is a token format; IdP is the system issuing/managing identity.
Q5. Does every Microservice authenticate the username and password?
Normally, no.
The identity system authenticates the user. Protected APIs validate the resulting access token and apply authorization policies.
Q6. Can an IdP authenticate Microservices?
Yes.
Microservices can have application/workload identities.
For example:
Order Service
     |
     | Client Credentials
     v
Authorization Server
     |
     | Access Token
     v
Payment Service
Q7. What is the difference between Identity Provider and Authorization Server?
Answer:
An Identity Provider focuses on establishing identity and authentication. An OAuth Authorization Server authorizes clients and issues access tokens.
A modern identity platform often performs both roles.
Short Interview Answer
An Identity Provider, or IdP, is a trusted identity system that authenticates users or applications and provides identity information or tokens that other applications can trust. In a microservices architecture, instead of every service implementing login, a centralized identity platform such as Microsoft Entra ID, Keycloak, Auth0, or Okta handles authentication and token issuance. Clients then send access tokens to protected APIs, which validate the token and apply their own authorization rules. IdPs also commonly provide capabilities such as OpenID Connect, OAuth 2.0, SSO, MFA, federation, and application/workload identities.
The easiest flow to remember:
               Identity Provider
                      |
                Authenticate
                      |
                 Issue Token
                      |
                      v
User/Service ------> Client
                      |
                 Access Token
                      |
                      v
                  Web API
                      |
                Validate Token
                      |
                      v
                 Authorize
Identity Provider establishes the trusted identity; the API decides what that identity is allowed to do.